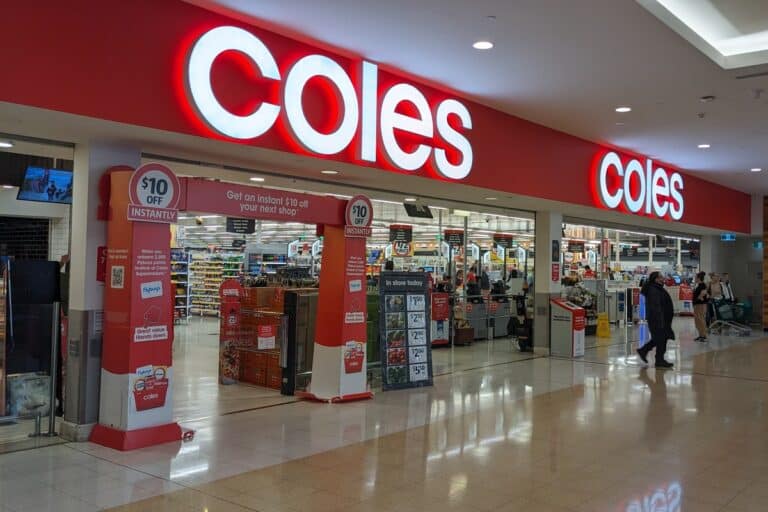

Coles Group is investigating a cybersecurity incident in Australia. In a 16 November filing to the Australian Securities Exchange, Coles said its stores and online grocery service continued to operate normally. It had found no evidence so far that customer, staff or supplier data had been compromised or taken.
Coles said it was working with the Australian Cyber Security Centre and external specialists to contain the incident and secure its systems. It did not identify the systems involved or say when the investigation would conclude.
The retailer said customers could continue using the Coles app and website. Its update also said gift cards were working and it had found no indication of an impact on Flybuys accounts.
Separately, Coles said a small number of Liquorland customers had reported problems with click-and-collect. It is investigating those reports and has not confirmed a link to the cybersecurity incident.
Coles is one of Australia’s largest supermarket chains. Its supplier update said partners did not need to take action at this stage, but urged them to be alert to suspicious requests for personal information. A supplier receiving an unexpected request to change bank details or share account credentials can check it through an established Coles contact before responding.
For grocery operators, the disclosure shows why trading continuity and data exposure need to be tracked separately. Recent refrigeration incidents in the UK food chain had a different operational impact. Coles has not reported comparable disruption to its supermarkets.
Coles said it would issue further updates as its investigation progresses. For trading partners, the next detail to watch is whether the company identifies any affected supplier systems or issues new instructions.
Editor’s note: Based on Coles Group’s 16 November 2026 ASX filing and its customer and supplier incident update.